

Cloud & AI
Give your team a controlled way to use managed applications, build custom workloads and operate approved cloud services. Choose the experience and operating model that fit your organization.


Cloud, AI, and Continuous Assurance for Aerospace and Defense
Use managed applications, build on approved cloud services, or continuously assess the infrastructure you already run. Liminaid brings cloud, AI, and agentic assurance together for sensitive aerospace and defense workloads.
Sensitive cloud and AI operations need more than infrastructure. Start with the work your team needs done, whether the environment is new or already running.
Give your team a controlled way to use managed applications, build custom workloads and operate approved cloud services. Choose the experience and operating model that fit your organization.
Assess the infrastructure you already run. Investigate access changes, identify observable gaps, recommend qualified improvements and maintain evidence without migrating workloads to a new platform.
Liminaid Assurance is designed for 24/7/365 AI-assisted assessment of authorized cloud and AI environments. Agents investigate changes, review effective access and recommend next steps. Defined technical checks verify observable controls and preserve evidence, with decisions and consequential actions under customer authority.
Connect resources, identities, relationships and approved requirements.
Trace access, configuration and telemetry changes to affected programs and applications.
Prioritize reviewed recommendations, use explicit approvals and maintain proof that corrections worked.
Use the application. Leave the platform work to us. Managed cloud and AI applications with guided setup and agreed operations.
Build your application on an approved foundation. Request qualified application, data and AI services without rebuilding every control.
Keep your expertise, tooling and authority. Integrate qualified platform services and evidence into mature engineering workflows.
Connect customer-approved export-control restrictions, CUI safeguards, cybersecurity requirements, and program obligations to the services, access, and evidence your workload needs.
Explore AWS GovCloud, Azure Government, and qualified Google Cloud configurations. Eligibility depends on the provider, service, region, workload, and operating arrangement. See how ITAR, EAR, CUI, and applicable cybersecurity requirements inform the approved scope →
Start with a managed application or develop your own workload using reviewed runtimes, data, storage, and supporting services. Choose the experience that fits your team rather than recreate the foundation.
Explore Platform Services →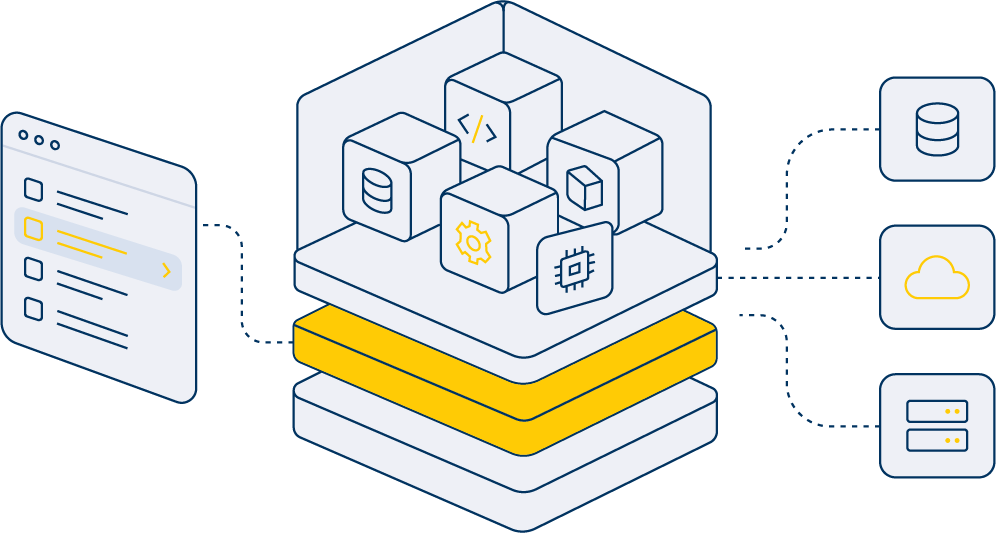
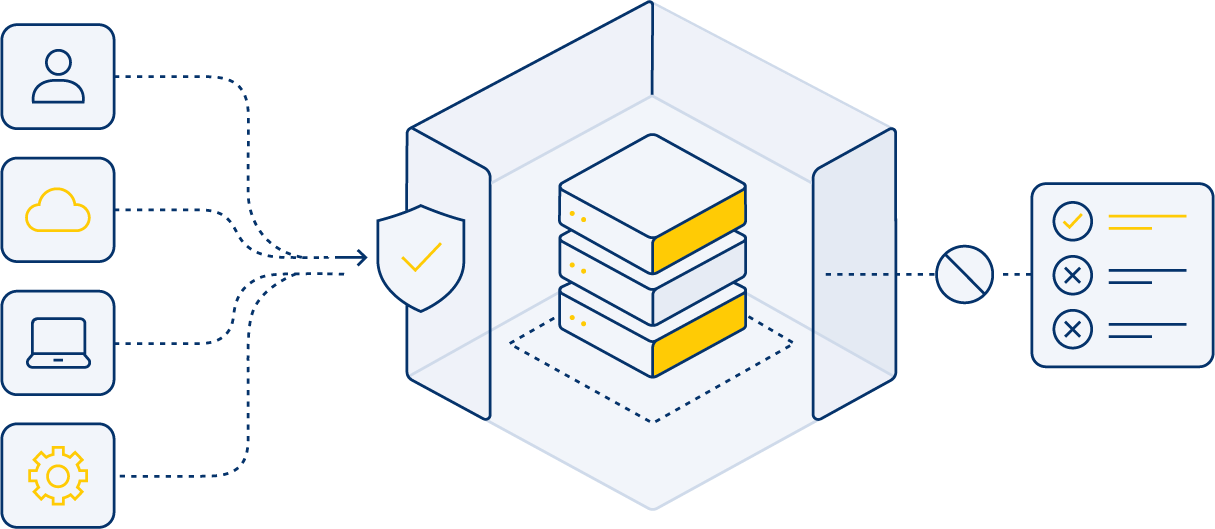
Translate customer-defined requirements into controls across identity, deployment, networking, and service access. Block disallowed actions where technically possible and surface changes that require review.
Explore Boundary Controls →Connect approved information sources, retrieval components, model endpoints, and tools through governed deployment patterns. Include prompts, outputs, and logs in the operating design.
Explore AI Governance →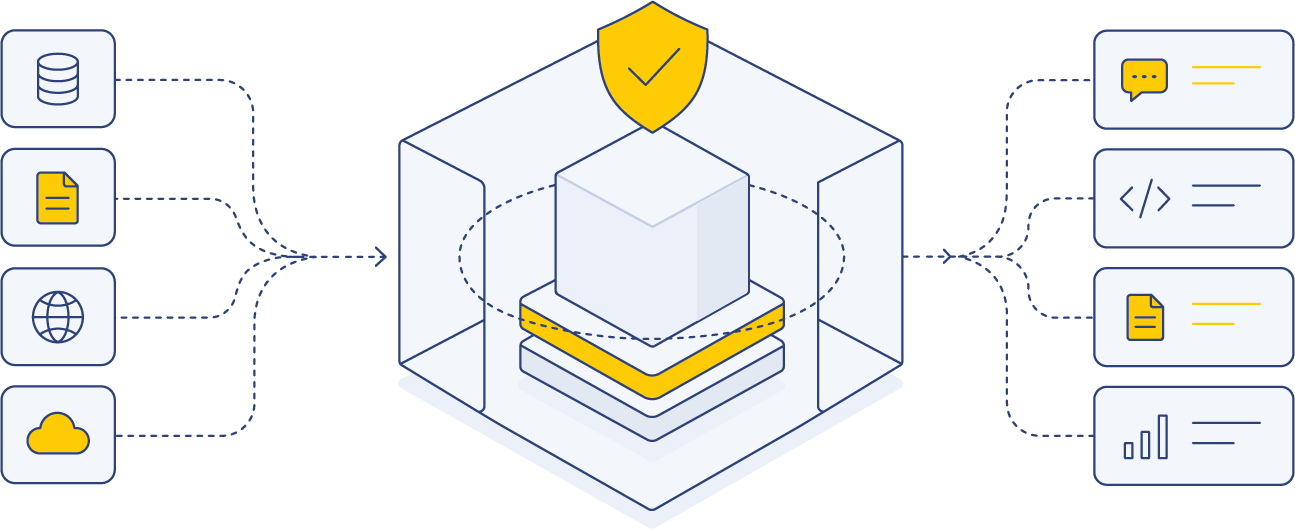
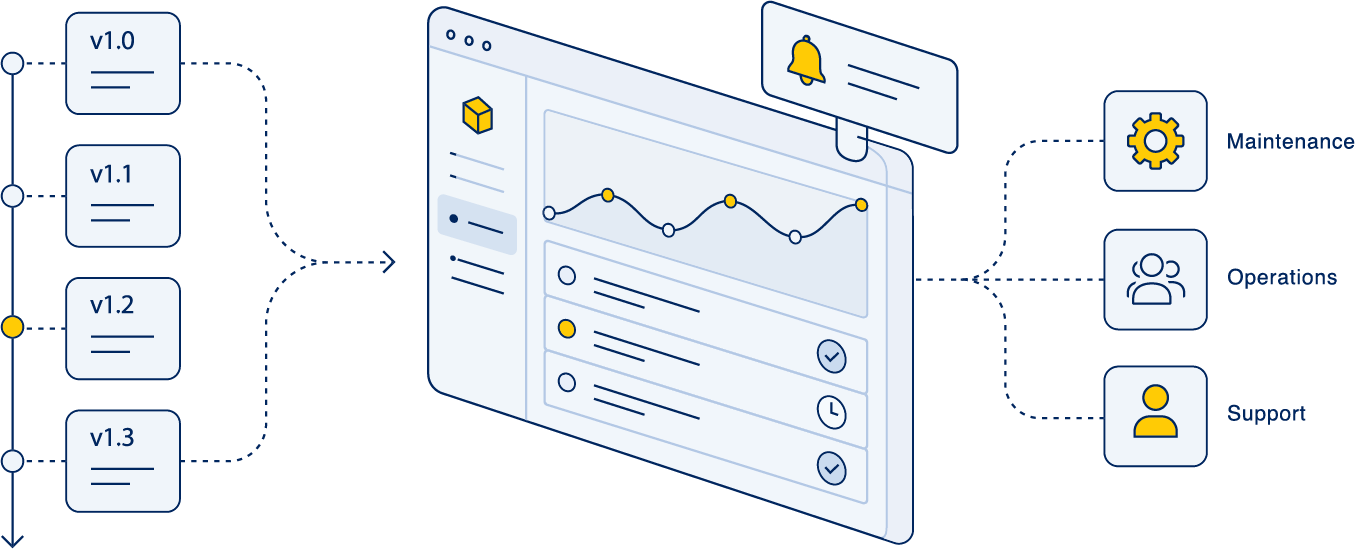
Assurance is designed to investigate observable access and configuration changes, recommend reviewed action, and verify corrections. Use it inside the agreed PaaS scope or independently across authorized existing environments.
Explore Liminaid Assurance →Give application buyers, developers, platform teams, and security leaders a clear starting point without forcing the same operating model on everyone.
Discuss a useful managed application with guided setup and agreed support, not a requirement to build software.
Own your application code while starting with approved services, deployment patterns, and embedded Assurance.
Assess existing cloud controls, investigate changing access, and maintain evidence without a platform migration.
Retain your toolchain and authority while integrating qualified patterns, policy interfaces, and evidence.
Connect approved requirements to technical controls and supporting evidence.
Choose the balance of ownership and operations that fits the organization.
Choose who owns the cloud environment and who operates the platform, independently of Ready, Build, or Control. Standalone Assurance remains available without selecting a PaaS model.
Liminaid provides the environment and operates the platform. Your team focuses on approved workloads.
Explore Managed Platform →Keep your cloud account, data, and final authority. Liminaid operates the platform within your environment.
Explore Managed BYOC →Deploy Liminaid in your environment and operate it with your own team, without standing Liminaid human administration.
Explore Private Edition →
Explore managed applications, an approved development platform, or Assurance of existing infrastructure. Let’s find the right scope and starting point for your team.
© 2026 Liminaid. All rights reserved.

